Why this is hard
Reaching a private system is no longer the hard part. Most AI models can now connect to a database or an API through a tunnel or a key. The hard part is control: who allowed this tool to read this data, for how long, and what did it read? A key pasted into a tool answers none of those questions.
What Substrait does
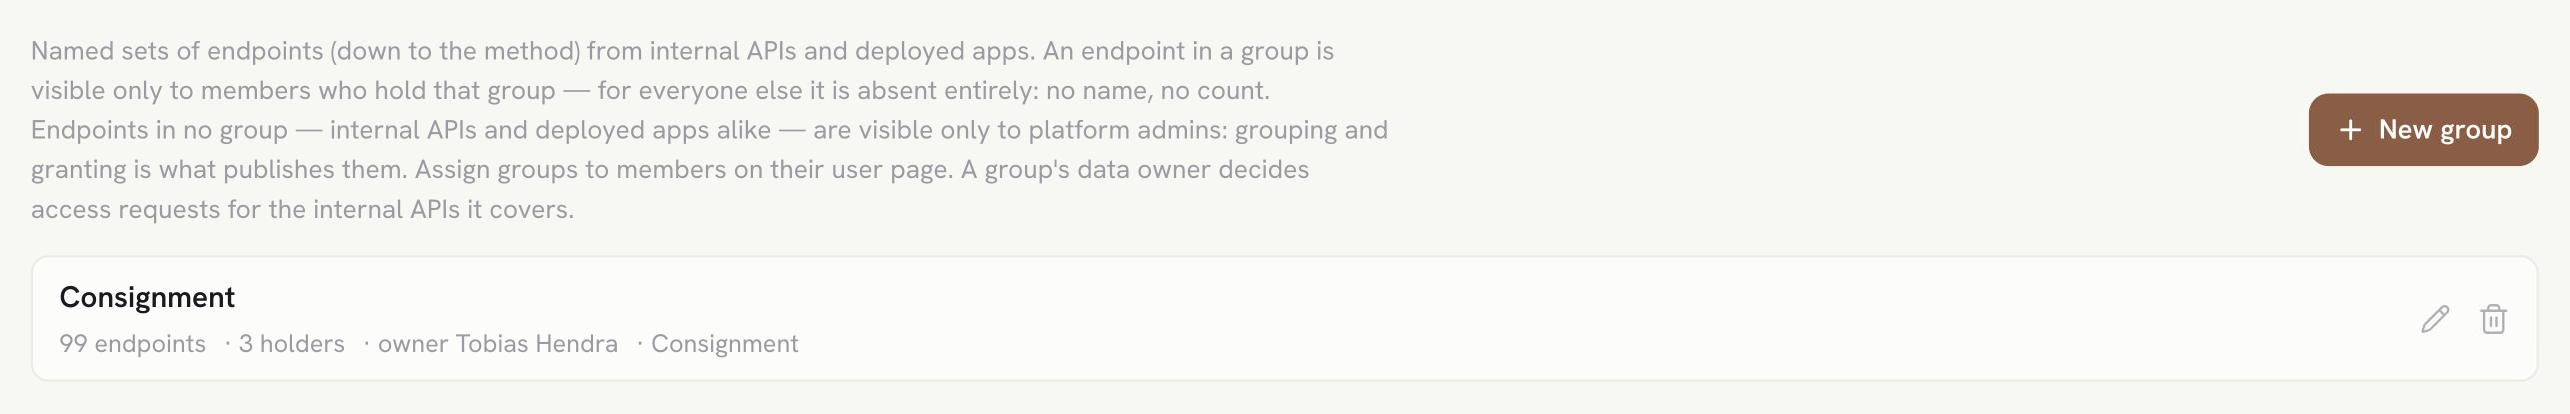
Data is grouped, and each group has an owner. An admin puts APIs, data sets and fields into data groups, such as finance or operations. Each data group has a data owner, who decides every request for its data.
Seeing and reading are two separate grants. Enrolment lets a person see which data exists and its shape, with no records. Authorisation lets a person or a tool read the data, once the data owner approves.
A tool gets its own grant. A tool’s access is approved separately from its builder’s access. It can never be wider than what the person who asked for it is enrolled to see. An approved grant stays with the tool when its owner leaves.
Every grant expires. Authorisations last for a set time, then the person or tool asks again. A data owner can also cap how often a tool may call, so a runaway tool slows down instead of stopping others.
One gateway for every source. Every call a tool makes to company data goes through Substrait’s gateway. The gateway checks the grant, attaches the credential and records the read. An ungranted call is refused with the name of the missing grant. Outbound traffic from a tool is denied unless a grant allows it.
What a tool can reach this way
| Source | How Substrait reaches it |
|---|---|
| Your systems’ APIs | Registered in the API Library, opened to a tool only after the data owner approves |
| Tools built on Substrait | Each tool’s API joins the library, closed until a data group grants it |
| Your data warehouse | Reviewed, parameterised and versioned data sets, never raw queries |
| Your reporting tools | Saved queries read through Substrait, with no reporting-tool key in the tool |
| Business systems | Connectors for SAP, Salesforce, Oracle, NetSuite and the Microsoft stack |